• Regeln für den Dokumente-Bereich:

    In den Börsenbereich gehören nur Angebote die bereits den Allgemeinen Regeln entsprechen.

    Allgemeines:

    Nicht erlaubt im Dokumente-Bereich sind:

    - indizierte Titel (inkl. Comics)
    - extremistische Werke, Zeitschriften und Comics (egal, welche Richtung)
    - jegliche Art von Pornographie
    - Anleitungen zu kriminellen Handlungen, gleich welcher Art
    - sadistische, menschenverachtende oder ähnliche Werke

    Nutzt den "Bedanken"-Button, bei Sammelthreads führen jegliche Kommentare, positiv wie negativ, sehr schnell zu einer Unübersichtlichkeit des Threads. Downmeldungen sind an den Uploader zu richten

    Vor dem Einstellen zu beachten:

    - Suchfunktion

    Vergewissert euch, dass es euer Dokument noch nicht im Board gibt, Doppelposts werden kommentarlos gelöscht. Ist es schon vorhanden, tragt es als Mirror im bestehenden Post ein.

    - Threadtitel

    Idealerweise ist sofort zu erkennen um was es sich handelt. Verseht euren Titel mit den relevanten Informationen, das hilft euch und damit auch uns und allen Suchenden erheblich weiter.

    Beispiel: [Thriller] Dan Brown - Inferno oder bei Magazinen:

    Computerbild - 14/2014 (es muss ersichtlich sein, um welche Ausgabe und welches Magazin es sich handelt)

    Folgende Präfixe stehen im Unterforum "Unterhaltung" zur Verfügung:

    [Humor]
    [Drama]
    [Erotik]
    [Fantasy]
    [Krimi]
    [Roman]
    [Thriller]
    [Horror]
    [Science Fiction]

    Inhalt des Beitrags:

    Folgende Pflichtangaben gilt es einzuhalten:

    - Autor
    - Titel
    - Präfix
    - Cover
    - Genre
    - Inhaltsbeschreibung
    - enthaltene Formate
    - Gesamtgröße des Downloads
    - Hoster
    - ggf. Passwort

    Nicht erlaubt sind alle Dateien, die den Download unnötig aufblähen um eine Affiliategrenze zu erreichen, wie zB. mp3-files, übergroße Bilder, etc.

    Ebenso nicht erlaubt sind sämtliche Dateien mit DRM, persönlichen Daten, etc., diese werden kommentarlos zu eurem eigenem Schutz gelöscht.

    Achtet bitte bei der Konvertierung der Formate auf die Lesbarkeit, ein epub, was nur einfach durch Calibre gejagt wird um ein PDF zu erhalten, ist zu 99% eben nicht lesbar. Wenn ihr es nicht könnt, dann lasst es besser oder lest euch ein, wie man es richtig macht.


    Unterforum Comics:

    Threadtitel:

    Ähnlich, wie bei Unterhaltung und Magazinen, sollte der Titel alle relevanten Informationen enthalten, hier bitte

    - den Titel des Comics
    - den Verlag (einige Comics sind in verschiedenen Verlagen erschienen)
    - das Erscheinungsjahr

    Erlaubt sind folgende Formate:

    - CBR
    - CBZ

    Grundsätzlich gilt: jede Version eines Comics erhält einen eigenen Thread, Ersteller eines Comics können ihre Bände gerne mit dem Zusatz (Original-Release) versehen.

    Bei Unsicherheiten zur korrekten Benennung bitte die Informationen von www.comicguide.de nutzen.

    Inhalt des Beitrags:

    Pflichtangaben hier sind:

    - Titel des Bandes und ggf. Nummer
    - Cover
    - falls bekannt technische Daten (DPI, Breite, Speicherqualität)
    - Größe des Downloads
    - Hoster
    - ggf. Passwort
    - falls bekannt Releasenamen
  • Bitte registriere dich zunächst um Beiträge zu verfassen und externe Links aufzurufen.

++ Premium IPTV ++ 7000 Live Sender ++ UHD Qualität ++ Mediathek mit 18.000 Inhalten ++


VenneTV


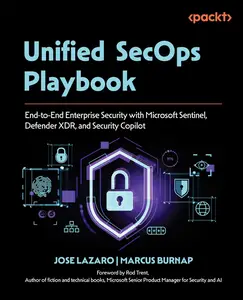
Unified SecOps Playbook End-to-end enterprise security with Microsoft Sentinel, Defender XDR, and Security Copilot

nakara

MyBoerse.bz Pro Member
8d6e71e383de82bcdf337dcf384c91b4.webp

Unified SecOps Playbook
by Jose Lazaro;Marcus Burnap;

English | 2025 | ISBN: 1837632863 | 473 pages | True EPUB | 33.41 MB​

A practical guide to modern cybersecurity using Microsoft tools, covering step-by-step setup, Zero Trust AI integration, and security framework alignment
Key Features
Deploy Microsoft Sentinel with end-to-end guidance, including CI/CD automation and scalable architecture
Integrate Security Copilot with Defender XDR to enable AI-driven threat detection and response
Implement Zero-Trust strategies and align with modern DevSecOps and cybersecurity frameworks
Purchase of the print or Kindle book includes a free PDF eBook
Book Description
In the evolving cybersecurity landscape, the integration of Microsoft Defender XDR and Security Copilot presents a game-changing approach to modern threat detection and response. With this book, you'll understand how these tools, in conjunction with Microsoft's extensive ecosystem, enable organizations to outpace emerging threats.
Starting with core XDR concepts, security frameworks, and Microsoft's competitive advantages in cybersecurity, you'll master the foundational aspects of deploying Microsoft Sentinel, configuring security infrastructure, and optimizing security operations using AI-driven tools. Advanced topics, including Zero-Trust strategies, DevSecOps integration, and partner programs, prepare you for increasingly sophisticated scenarios in Microsoft cloud security. You'll also explore practical deployment workflows, covering cost analysis, role-based access configurations, and fast-tracked Sentinel deployment using CI/CD pipelines.
By the end of this book, you'll have gained insights into security automation, threat detection, and AI integration with Security Copilot for optimized operations and have the confidence to implement and manage Microsoft Defender XDR and Sentinel in complex environments, driving scalable and secure solutions.
What you will learn
Deploy Microsoft Sentinel with RBAC, governance, and financial planning
Align security programs with Zero Trust and global frameworks
Automate assessments with ScubaGear, Maester, and Azure DevOps
Build secure Sentinel foundations with Entra ID, PIM, and management groups
Onboard customers and partners via Azure Lighthouse and GDAP
Master the Sentinel workflow backbone: KQL, detections, automation, MITRE ATT&CK
Accelerate rollouts using FastTrack deployment and CI/CD pipelines
Harness Security Copilot for AI-assisted detection and investigation
Who this book is for
This book is for you if you have a solid understanding of Microsoft security products and Azure and are now looking to expand your expertise by incorporating Microsoft Sentinel. Security experts using alternative SIEM tools who want to adopt Microsoft Sentinel as an additional or replacement service will also find this book useful.
Table of Contents
Microsoft Defender XDR in the Era of Copilots
Aligning with Cybersecurity Frameworks
Microsoft Security for Partners
Core Foundations - Initial Setup, Strategic Financial Planning, and Business Insights
Getting Ready for Action - Assess Your Microsoft 365 Tenant
Foundational Architecture and Secure Access for Sentinel Deployments for MSSPs
Customer Onboarding - The Power of Azure Lighthouse
Joining the Dots - Microsoft Sentinel Deployment Workflow
Microsoft Sentinel Fast-Track Deployment Options and CI/CD Pipelines
Activate, Configure, Deploy - Your First Steps with Security Copilot


​
Links are Interchangeable - Single Extraction​
 
Zurück
Oben Unten