• Regeln für den Video-Bereich:

    In den Börsenbereich gehören nur Angebote die bereits den Allgemeinen Regeln entsprechen.

    Einteilung

    - Folgende Formate gehören in die angegeben Bereiche:
    - Filme: Encodierte Filme von BluRay, DVD, R5, TV, Screener sowie Telesyncs im Format DivX, XviD und x264.
    - DVD: Filme im Format DVD5, DVD9 und HD2DVD.
    - HD: Encodierte Filme mit der Auflösung 720p oder darüber von BluRay, DVD, R5, TV, Screener sowie Telesyncs im Format x264.
    - 3D: Encodierte Filme von BluRay, die in einem 3D Format vorliegen. Dies gilt auch für Dokus, Animation usw.
    - Serien: Cartoon/Zeichentrick, Anime, Tutorials, Dokumentationen, Konzerte/Musik, Sonstiges sind demnach in die entsprechenden Bereiche einzuordnen, auch wenn sie beispielsweise im High Definition-Format oder als DVD5/DVD9/HD2DVD vorliegen. Ausnahme 3D.
    - Bereich Englisch: Englische Releases gehören immer in diesen Bereich.
    - Bereich Talk: Der Bereich, in dem über die Releases diskutiert werden kann, darf, soll und erwünscht ist.


    Angebot/Beitrag erstellen

    - Ein Beitrag darf erst dann erstellt werden, wenn der Upload bei mindestens einem OCH komplett ist. Platzhalter sind untersagt.
    - Bei einem Scenerelease hat der Threadtitel ausschließlich aus dem originalen, unveränderten Releasenamen zu bestehen. Es dürfen keine Veränderungen wie z.B. Sterne, kleine Buchstaben o.ä. vorgenommen werden. Ausnahme Serienbörse:
    - Bei einem Sammelthread für eine Staffel entfällt aus dem Releasename natürlich der Name der Folge. Beispiel: Die Simpsons S21 German DVDRip XviD - ITG
    - Dementsprechend sind also u.a. verboten: Erweiterungen wie "Tipp", "empfehlenswert", "only", "reup", usw. / jegliche andere Zusatzinformation oder Ergänzung, welche nicht in obiger Beschreibung zu finden ist.

    Aufbau des Angebots und Threadtitel

    Der Titel nach folgendem Muster erstellt zu werden. <Name> [3D] [Staffel] [German] <Jahr> <Tonspur> [DL] [Auflösung] <Quelle> <Codec> - <Group>
    Beispiel: The Dark Knight German 2008 AC3 DVDRip XviD - iND
    Beispiel: The Dark Knight 2008 DTS DL BDRip x264 - iND
    Beispiel: The Dark Knight 2008 AC3 DL BDRip XviD - iND
    Beispiel: The Dark Knight German 2008 AC3 720p BluRay x264 iND
    Beispiel: The Dark Knight 2008 DTS DL 1080p BluRay x264 iND
    Beispiel: Die Simpsons S01 German AC3 DVDRip XviD iND
    Beispiel: Die Simpsons S20 German AC3 720p BluRay x264 iND
    Beispiel: Sword Art Online II Ger Sub 2014 AAC 1080p WEBRip x264 - peppermint
    Entsprechend sind also u.a. verboten: Sonderzeichen wie Klammern, Sterne, Ausrufezeichen, Unterstriche, Anführungszeichen / Erweiterungen wie "Tipp", "empfehlenswert", "only", "reup", usw. / jegliche andere Zusatzinformation oder Ergänzung, welche nicht in obiger Beschreibung zu finden ist
    Ausnahmen hiervon können in den Bereichen geregelt sein.

    Die Beiträge sollen wie folgt aufgebaut werden:
    Überschrift entspricht dem Threadtitel
    Cover
    kurze Inhaltsbeschreibung
    Format, Größe, Dauer sind gut lesbar für Downloader außerhalb des Spoilers zu vermerken
    Nfo sind immer Anzugeben und selbige immer im Spoiler in Textform.
    Sind keine Nfo vorhanden z.B. Eigenpublikationen, sind im Spoiler folgende Dateiinformationen zusätzlich anzugeben :
    Quelle
    Video (Auflösung und Bitrate)
    Ton (Sprache, Format und Bitrate der einzelnen Spuren)
    Untertitel (sofern vorhanden)
    Hosterangabe in Textform außerhalb eines Spoiler mit allen enthaltenen Hostern.
    Bei SD kann auf diese zusätzlichen Dateiinformationen verzichtet werden.

    Alle benötigten Passwörter sind, sofern vorhanden, in Textform im Angebot anzugeben.
    Spoiler im Spoiler mit Kommentaren :"Schon Bedankt?" sind unerwünscht.


    Releases

    - Sind Retail-Release verfügbar, sind alle anderen Variationen untersagt. Ausnahmen: Alle deutschen Retail-Release sind CUT, in diesem Fall sind dubbed UNCUT-Release zulässig.
    - Im Serien-Bereich gilt speziell: Wenn ein Retail vor Abschluss einer laufenden Staffel erscheint, darf diese Staffel noch zu Ende gebracht werden.62
    - Gleiche Releases sind unbedingt zusammenzufassen. Das bedeutet, es ist zwingend erforderlich, vor dem Erstellen eines Themas per Suchfunktion zu überprüfen, ob bereits ein Beitrag mit demselben Release besteht. Ist dies der Fall, ist der bereits vorhandene Beitrag zu verwenden.
    - P2P und Scene Releases dürfen nicht verändert oder gar unter einem iND Tag eingestellt werden.


    Support, Diskussionen und Suche

    - Supportanfragen sind entweder per PN oder im Bereich Talk zu stellen.
    - Diskussionen und Bewertungen sind im Talk Bereich zu führen. Fragen an die Uploader haben ausschließlich via PN zu erfolgen, und sind in den Angeboten untersagt.
    - Anfragen zu Upload-Wünschen sind nur im Bereich Suche Video erlaubt. Antworten dürfen nur auf Angebote von MyBoerse.bz verlinkt werden.


    Verbote

    - Untersagt sind mehrere Formate in einem einzigen Angebotsthread, wie beispielsweise das gleichzeitige Anbieten von DivX/XviD, 720p und 1080p in einem Thread. Pro Format, Release und Auflösung ist ein eigener Thread zu eröffnen.
    - Grundsätzlich ebenso verboten sind Dupes. Uploader haben sich an geeigneter Stelle darüber zu informieren, ob es sich bei einem Release um ein Dupe handelt.
    - Gefakte, nur teilweise lauffähige oder unvollständige Angebote sind untersagt. Dies gilt auch für eigene Publikationen, die augenscheinlich nicht selbst von z.B. einer DVD gerippt wurden. Laufende Serien, bei denen noch nicht alle Folgen verfügbar sind, dürfen erstellt und regelmäßig geupdatet werden.
    - Untersagt sind Angebote, welche nur und ausschließlich in einer anderen Sprache als deutsch oder englisch vorliegen. Ausnahmen sind VORHER mit den Moderatoren zu klären.


    Verstoß gegen die Regeln

    - Angebote oder Beiträge, die gegen die Forenregeln verstoßen, sind über den "Melden"-Button im Beitrag zu melden.
  • Bitte registriere dich zunächst um Beiträge zu verfassen und externe Links aufzurufen.

++ Premium IPTV ++ 7000 Live Sender ++ UHD Qualität ++ Mediathek mit 18.000 Inhalten ++


VenneTV


Practical Auth0 Login, APIs & Enterprise SSO

babymore87

MyBoerse.bz Pro Member
e49f77d9a91dbafe710d13b9b4fda26c.webp

Free Download Practical Auth0 Login, APIs & Enterprise SSO
Published 8/2026
Created by Dr. Amar Massoud
MP4 | Video: h264, 1920x1080 | Audio: AAC, 44.1 KHz, 2 Ch
Level: Intermediate | Genre: eLearning | Language: English | Duration: 60 Lectures ( 4h 56m ) | Size: 4 GB

Universal Login, OAuth 2.0, token validation, Actions, Organizations and SAML SSO on a free tenant.
What you'll learn
⚡ Implement Universal Login in a Next.js 15 app with correct session, cookie and logout handling
⚡ Trace an OAuth 2.0 / OIDC flow end to end and choose the right grant for any client type
⚡ Validate a JWT correctly - signature, issuer, audience, expiry, algorithm - and spot the antipatterns
⚡ Secure an API with audiences, scopes and Auth0 RBAC, and explain where RBAC stops scaling
⚡ Extend the login pipeline with Actions: namespaced claims, external calls, deny rules, step-up
⚡ Deliver B2B multi-tenancy with Organizations, org-scoped roles and enterprise SAML SSO
⚡ Harden a tenant with MFA, step-up authentication, passkeys and attack protection
⚡ Operate identity in production: log streams, Terraform config-as-code, tenant promotion, user migration
⚡ Recognise why Rules and Hooks are ending, and write Actions instead
⚡ Migrate users off a legacy password store without forcing a single password reset
Requirements
❗ Comfortable building a basic web application and a REST API in JavaScript
❗ Working knowledge of Node.js and npm
❗ Familiarity with HTTP - requests, responses, headers, cookies, redirects
❗ A free Auth0 account (no credit card required - the sign-up is covered in the course)
❗ No prior identity, OAuth or security experience is assumed
Description
This course contains the use of artificial intelligence.
Most Auth0 material stops at the moment the login button works. This one keeps going - through token validation, API authorization, the extensibility pipeline, B2B multi-tenancy, enterprise SSO, and the operational work that keeps an identity system alive once real customers depend on it.
You will follow one company the whole way.Halcyon Travel is a booking platform with two products: a consumer app used by travellers, and a corporate travel product sold to companies. They rolled their own authentication in year one - bcrypt, a users table, hand-signed tokens, a signing key nobody has dared rotate since 2021. It creaks. Then a 4,000-seat enterprise prospect makes SAML single sign-on a contract condition, and the whole thing has to be rebuilt properly. Every concept in the course arrives because Halcyon hits a problem that needs it.
What the course covers
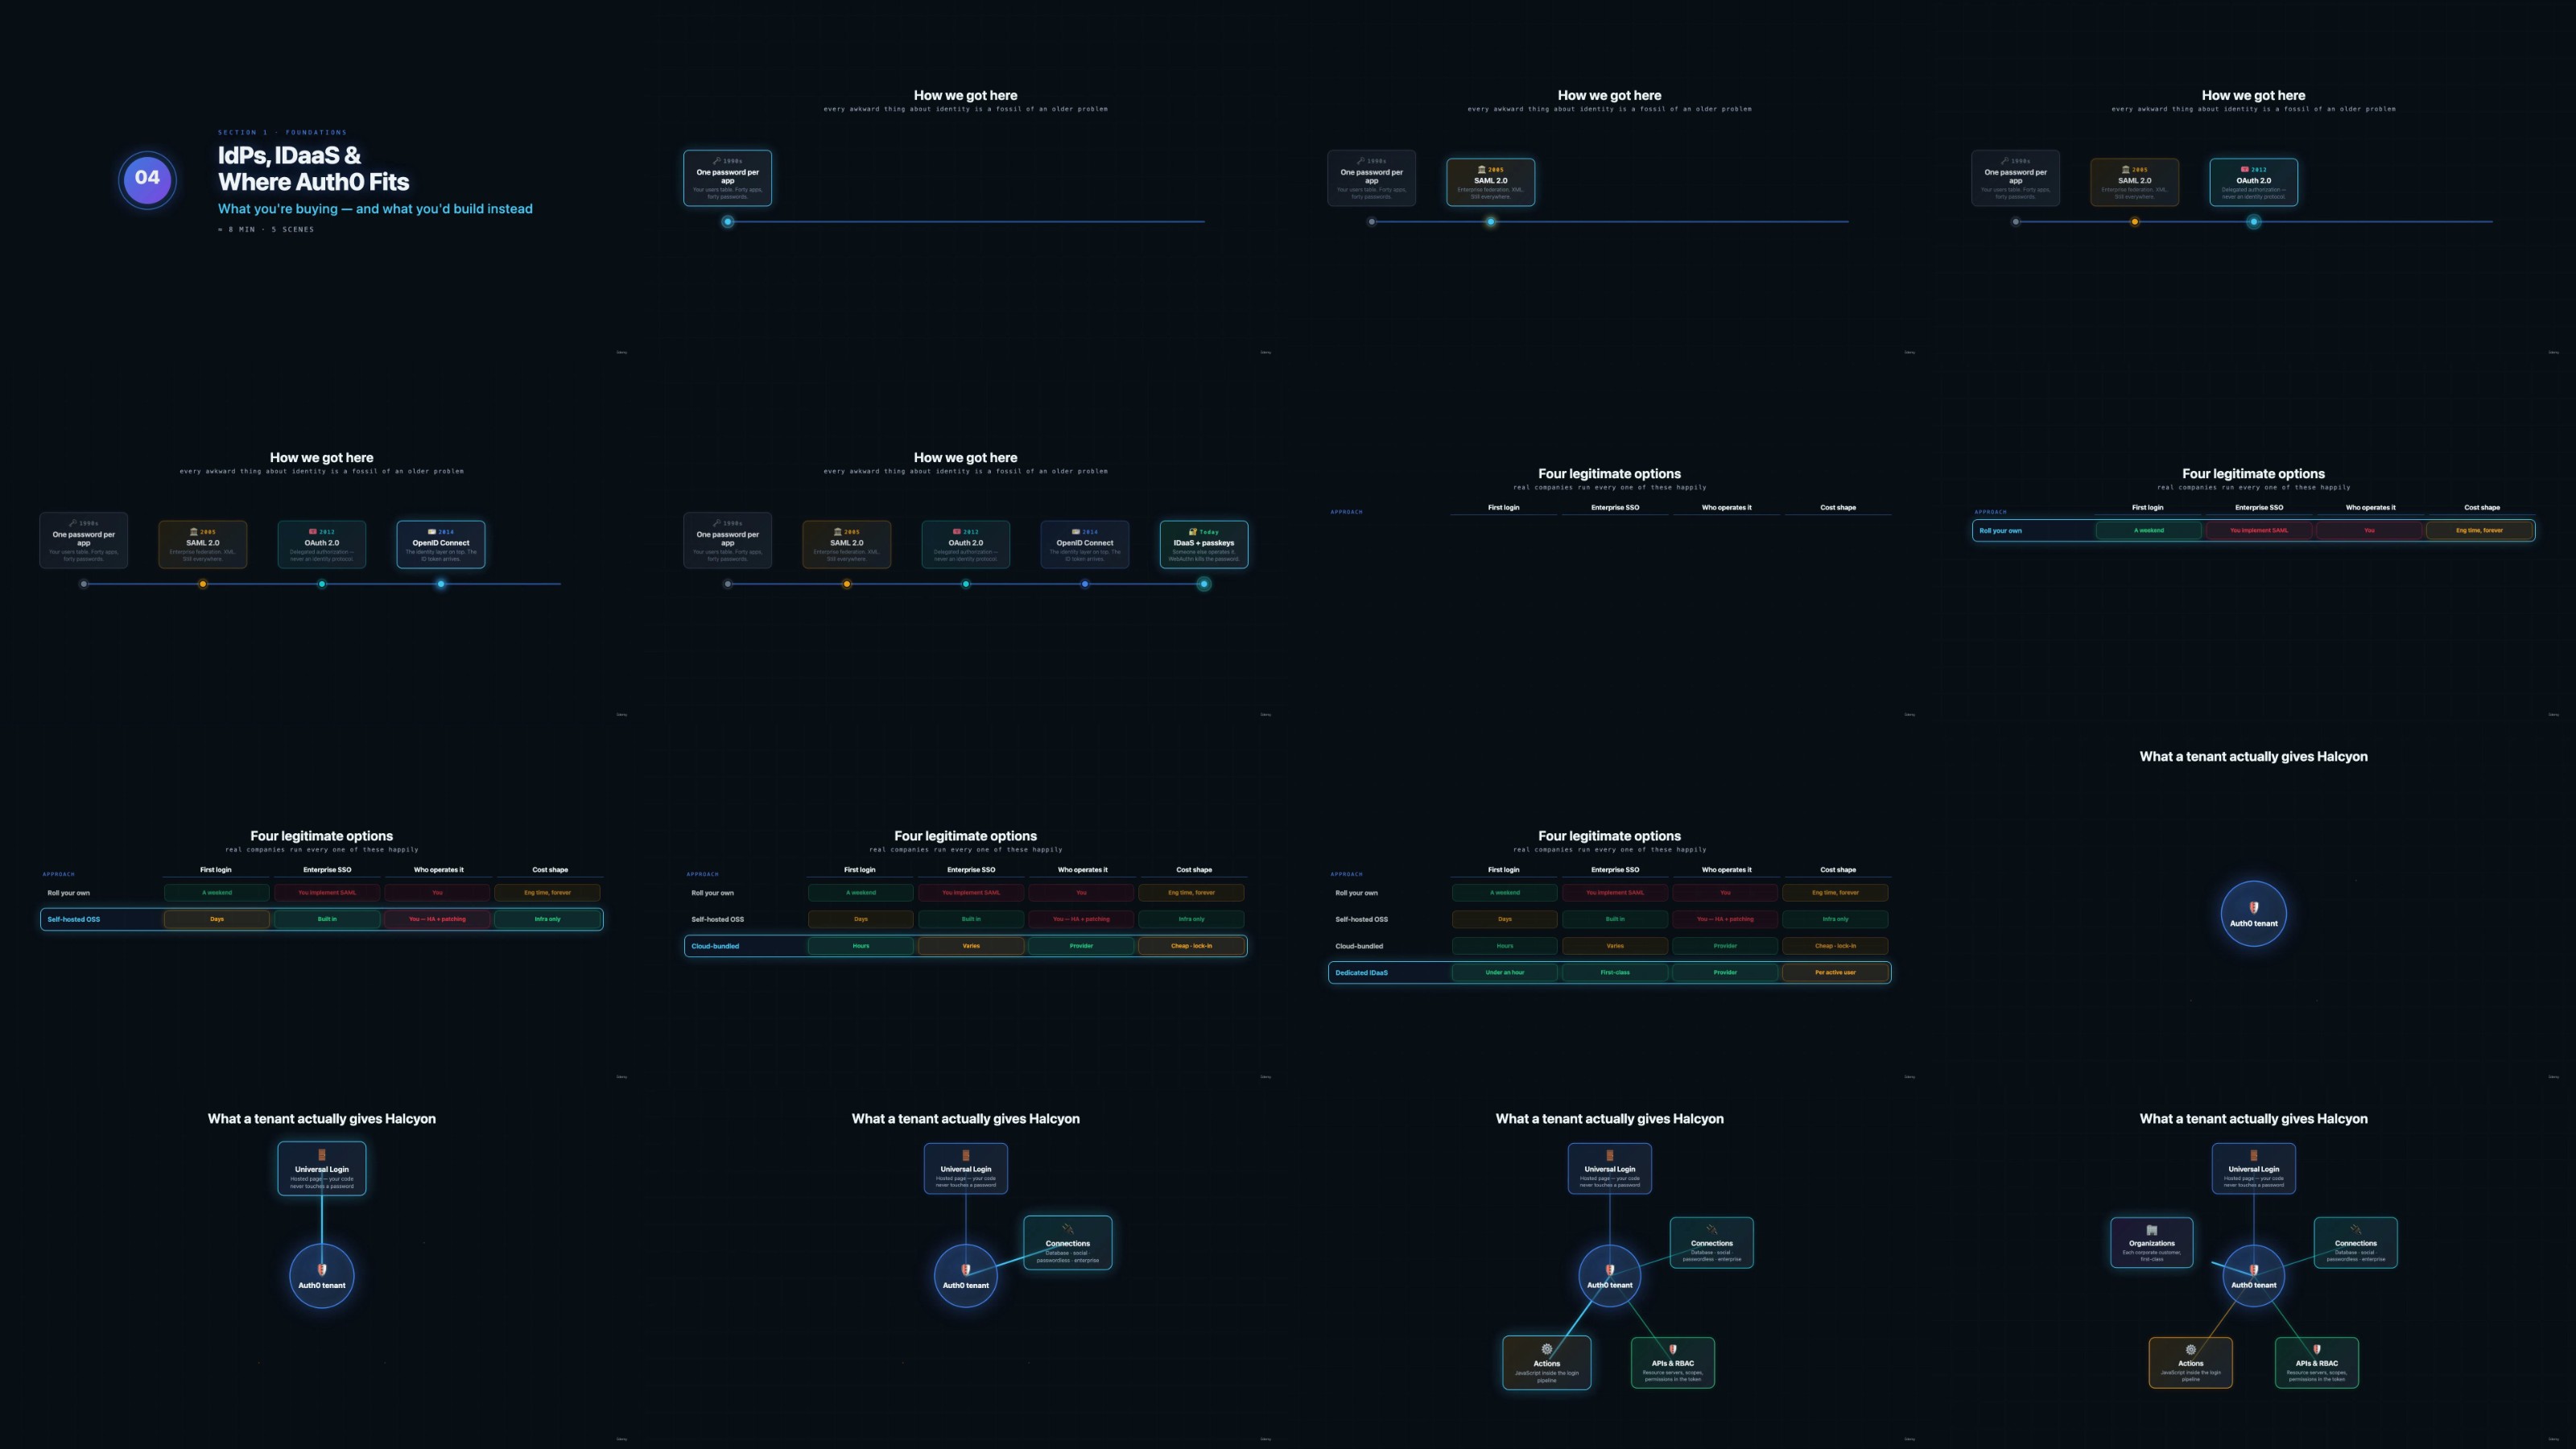
✨Foundations - authentication vs authorization, where Auth0 sits in the identity landscape, tenants, application types, connections, and the two APIs you will live in
✨OAuth 2.0 and OIDC properly - the authorization code flow step by step, PKCE and why public clients need it, client credentials, refresh token rotation, the flows you should never use, and the discovery and JWKS documents that make it all self-describing
✨Universal Login in Next.js - wiring the Auth0 Next.js SDK v4 with its middleware-mounted routes, sessions and rolling cookies, protecting server components and server actions, federated logout, and branding the login page
✨Tokens - what ID, access and refresh tokens are actually for, the anatomy of a JWT, how to validate one correctly (signature, issuer, audience, expiry, algorithm), why your access token might be opaque, and the antipatterns that cause real breaches
✨Securing an API - registering a resource server, requesting and enforcing scopes, protecting Express routes, Auth0 RBAC, the difference between roles, scopes and permissions, and an honest look at where RBAC stops scaling
✨Actions - the extensibility model that replaces Rules and Hooks before their18 November 2026 end of life: triggers, the event and api objects, namespaced custom claims, external calls and secrets, testing and deployment
✨B2B: Organizations and enterprise SSO - the multi-tenancy problem, organization login flows, invitations and just-in-time membership, org-scoped roles, SAML and OIDC enterprise connections to Okta and Entra ID, and a full enterprise onboarding runbook
✨Production hardening - MFA, step-up authentication for high-risk actions, passkeys and passwordless, attack protection, custom domains, and the classic session vulnerabilities
✨Operations - logs and log streams, configuration as code with the Auth0 CLI and Terraform provider, dev to staging to production promotion, and migrating users off a legacy store without asking anyone to reset a password
You also get to do the work, not just watch it
✨10 auto-graded coding exercises that run in your browser - build a PKCE challenge, validate an ID token, screen a batch of hostile tokens, write scope-checking middleware, author Action handlers. Each one fails you for the specific mistake the lecture warned about, not just for a wrong answer
✨12 hands-on labs against your own free tenant, each with a self-check script that tells you what is wrong and where to look. You will trace an authorization code flow by hand, secure a real API, deploy an Action, stand up two organizations, and federate SAML between two tenants
✨10 section quizzes and a 30-question final exam, scenario-based rather than recall-based - most describe something going wrong and ask you to identify why
✨A two-part capstone: Halcyon's complete identity stack, consumer and enterprise, with a migration plan underneath both
How it is taught. Sixty lectures of motion-driven explanation - animated protocol flows, architecture diagrams that build as they are described, and token payloads dissected on screen. No background music. No wall of bullet points read aloud.
Everything runs free. The Auth0 Free plan covers the tenant, and the enterprise SSO material uses a second free tenant as the identity provider. No credit card is required at any point.
The course closes with a capstone brief: Halcyon's complete identity stack, consumer and enterprise, plus the migration plan underneath both - specified as a business problem with three constraints rather than a list of steps to copy.
Who this course is for
⭐ Full-stack and backend developers who have been handed a ticket that says "add login"
⭐ Platform and security engineers who own an identity system and want to understand it properly
⭐ Developers whose product just sold to an enterprise customer demanding SAML SSO
⭐ Anyone maintaining Auth0 Rules or Hooks who needs to move to Actions before the 2026 EOL
⭐ Engineers who can wire up a login form but could not explain what the audience claim is for
Homepage
Recommend Download Link Hight Speed | Please Say Thanks Keep Topic Live
No Password - Links are Interchangeable

 

765093431_yxusj-c821cb16xu2j.jpg

Practical Auth0: Login, APIs & Enterprise SSO
MP4 | Video: h264, 1920x1080 | Audio: AAC, 44.1 KHz, 2 Ch
Level: Intermediate | Genre: eLearning | Language: English | Duration: 4h 56m | Size: 4 GB​

Most Auth0 material stops at the moment the login button works. This one keeps going - through token validation, API authorization, the extensibility pipeline, B2B multi-tenancy, enterprise SSO, and the operational work that keeps an identity system alive once real customers depend on it.

You will follow one company the whole way. Halcyon Travel is a booking platform with two products: a consumer app used by travellers, and a corporate travel product sold to companies. They rolled their own authentication in year one - bcrypt, a users table, hand-signed tokens, a signing key nobody has dared rotate since 2021. It creaks. Then a 4,000-seat enterprise prospect makes SAML single sign-on a contract condition, and the whole thing has to be rebuilt properly. Every concept in the course arrives because Halcyon hits a problem that needs it.

What the course covers

Foundations - authentication vs authorization, where Auth0 sits in the identity landscape, tenants, application types, connections, and the two APIs you will live in
OAuth 2.0 and OIDC properly - the authorization code flow step by step, PKCE and why public clients need it, client credentials, refresh token rotation, the flows you should never use, and the discovery and JWKS documents that make it all self-describing
Universal Login in Next.js - wiring the Auth0 Next.js SDK v4 with its middleware-mounted routes, sessions and rolling cookies, protecting server components and server actions, federated logout, and branding the login page
Tokens - what ID, access and refresh tokens are actually for, the anatomy of a JWT, how to validate one correctly (signature, issuer, audience, expiry, algorithm), why your access token might be opaque, and the antipatterns that cause real breaches
Securing an API - registering a resource server, requesting and enforcing scopes, protecting Express routes, Auth0 RBAC, the difference between roles, scopes and permissions, and an honest look at where RBAC stops scaling
Actions - the extensibility model that replaces Rules and Hooks before their 18 November 2026 end of life: triggers, the event and api objects, namespaced custom claims, external calls and secrets, testing and deployment
B2B: Organizations and enterprise SSO - the multi-tenancy problem, organization login flows, invitations and just-in-time membership, org-scoped roles, SAML and OIDC enterprise connections to Okta and Entra ID, and a full enterprise onboarding runbook
Production hardening - MFA, step-up authentication for high-risk actions, passkeys and passwordless, attack protection, custom domains, and the classic session vulnerabilities
Operations - logs and log streams, configuration as code with the Auth0 CLI and Terraform provider, dev to staging to production promotion, and migrating users off a legacy store without asking anyone to reset a password

You also get to do the work, not just watch it

10 auto-graded coding exercises that run in your browser - build a PKCE challenge, validate an ID token, screen a batch of hostile tokens, write scope-checking middleware, author Action handlers. Each one fails you for the specific mistake the lecture warned about, not just for a wrong answer
12 hands-on labs against your own free tenant, each with a self-check script that tells you what is wrong and where to look. You will trace an authorization code flow by hand, secure a real API, deploy an Action, stand up two organizations, and federate SAML between two tenants
10 section quizzes and a 30-question final exam, scenario-based rather than recall-based - most describe something going wrong and ask you to identify why
A two-part capstone: Halcyon's complete identity stack, consumer and enterprise, with a migration plan underneath both

yxusj-4-Id-Ps-IDaa-S-Where-Auth0-Fits.jpg

765094161_yxusj-9w72m21keks8.jpg

 
Zurück
Oben Unten