




AgentofHeart
MyBoerse.bz Pro Member

Application Security & Monitoring for Software Engineering
MP4 | Video: h264, 1920x1080 | Audio: AAC, 44.1 KHz, 2 Ch
Genre: eLearning | Language: English (US) | Duration: 4 h | Size: 1.59 GB
Application Security & Monitoring for Software Engineering
In today's digital world,
building software that simply works is no longer enough-it must also be secure, reliable, and continuously monitored.
Modern applications face threats such as SQL Injection, Cross-Site Scripting (XSS), vulnerable dependencies, insecure secrets, and other application-level attacks.
Application Security & Monitoring: DevSecOps, OWASP & Secure Software Development
is a comprehensive course designed to help you understand how to
design, develop, test, secure, monitor, and maintain modern applications
throughout the software development lifecycle.
You will learn how security can be integrated into development and operations from the beginning, transforming security from a final-stage activity into a
continuous part of software development
.
Secure Application Development
The course begins with the foundations of
Application Security, Security by Design, and DevSecOps
. You will understand why security should be considered during architecture, development, testing, deployment, and maintenance.
You will explore:
Application Security Fundamentals
Security by Design
DevSecOps
Vulnerability Scanning
Threat Modeling
Threat Monitoring
Security Concepts and Terminology
The goal is to develop a
security-first mindset
and understand how development, security, and operations teams can work together to build safer applications.
Security Testing & Mitigation Strategies
Security testing is a critical part of secure software development. You will explore modern techniques for identifying and mitigating vulnerabilities before attackers can exploit them.
You will learn about:
SAST - Static Application Security Testing
DAST - Dynamic Application Security Testing
Secure Code Review
Vulnerability Analysis
Runtime Protection
SCA - Software Composition Analysis
Continuous Security Analysis
You will understand how source-code analysis, dynamic testing, dependency analysis, and runtime protection contribute to a
continuous security strategy
.
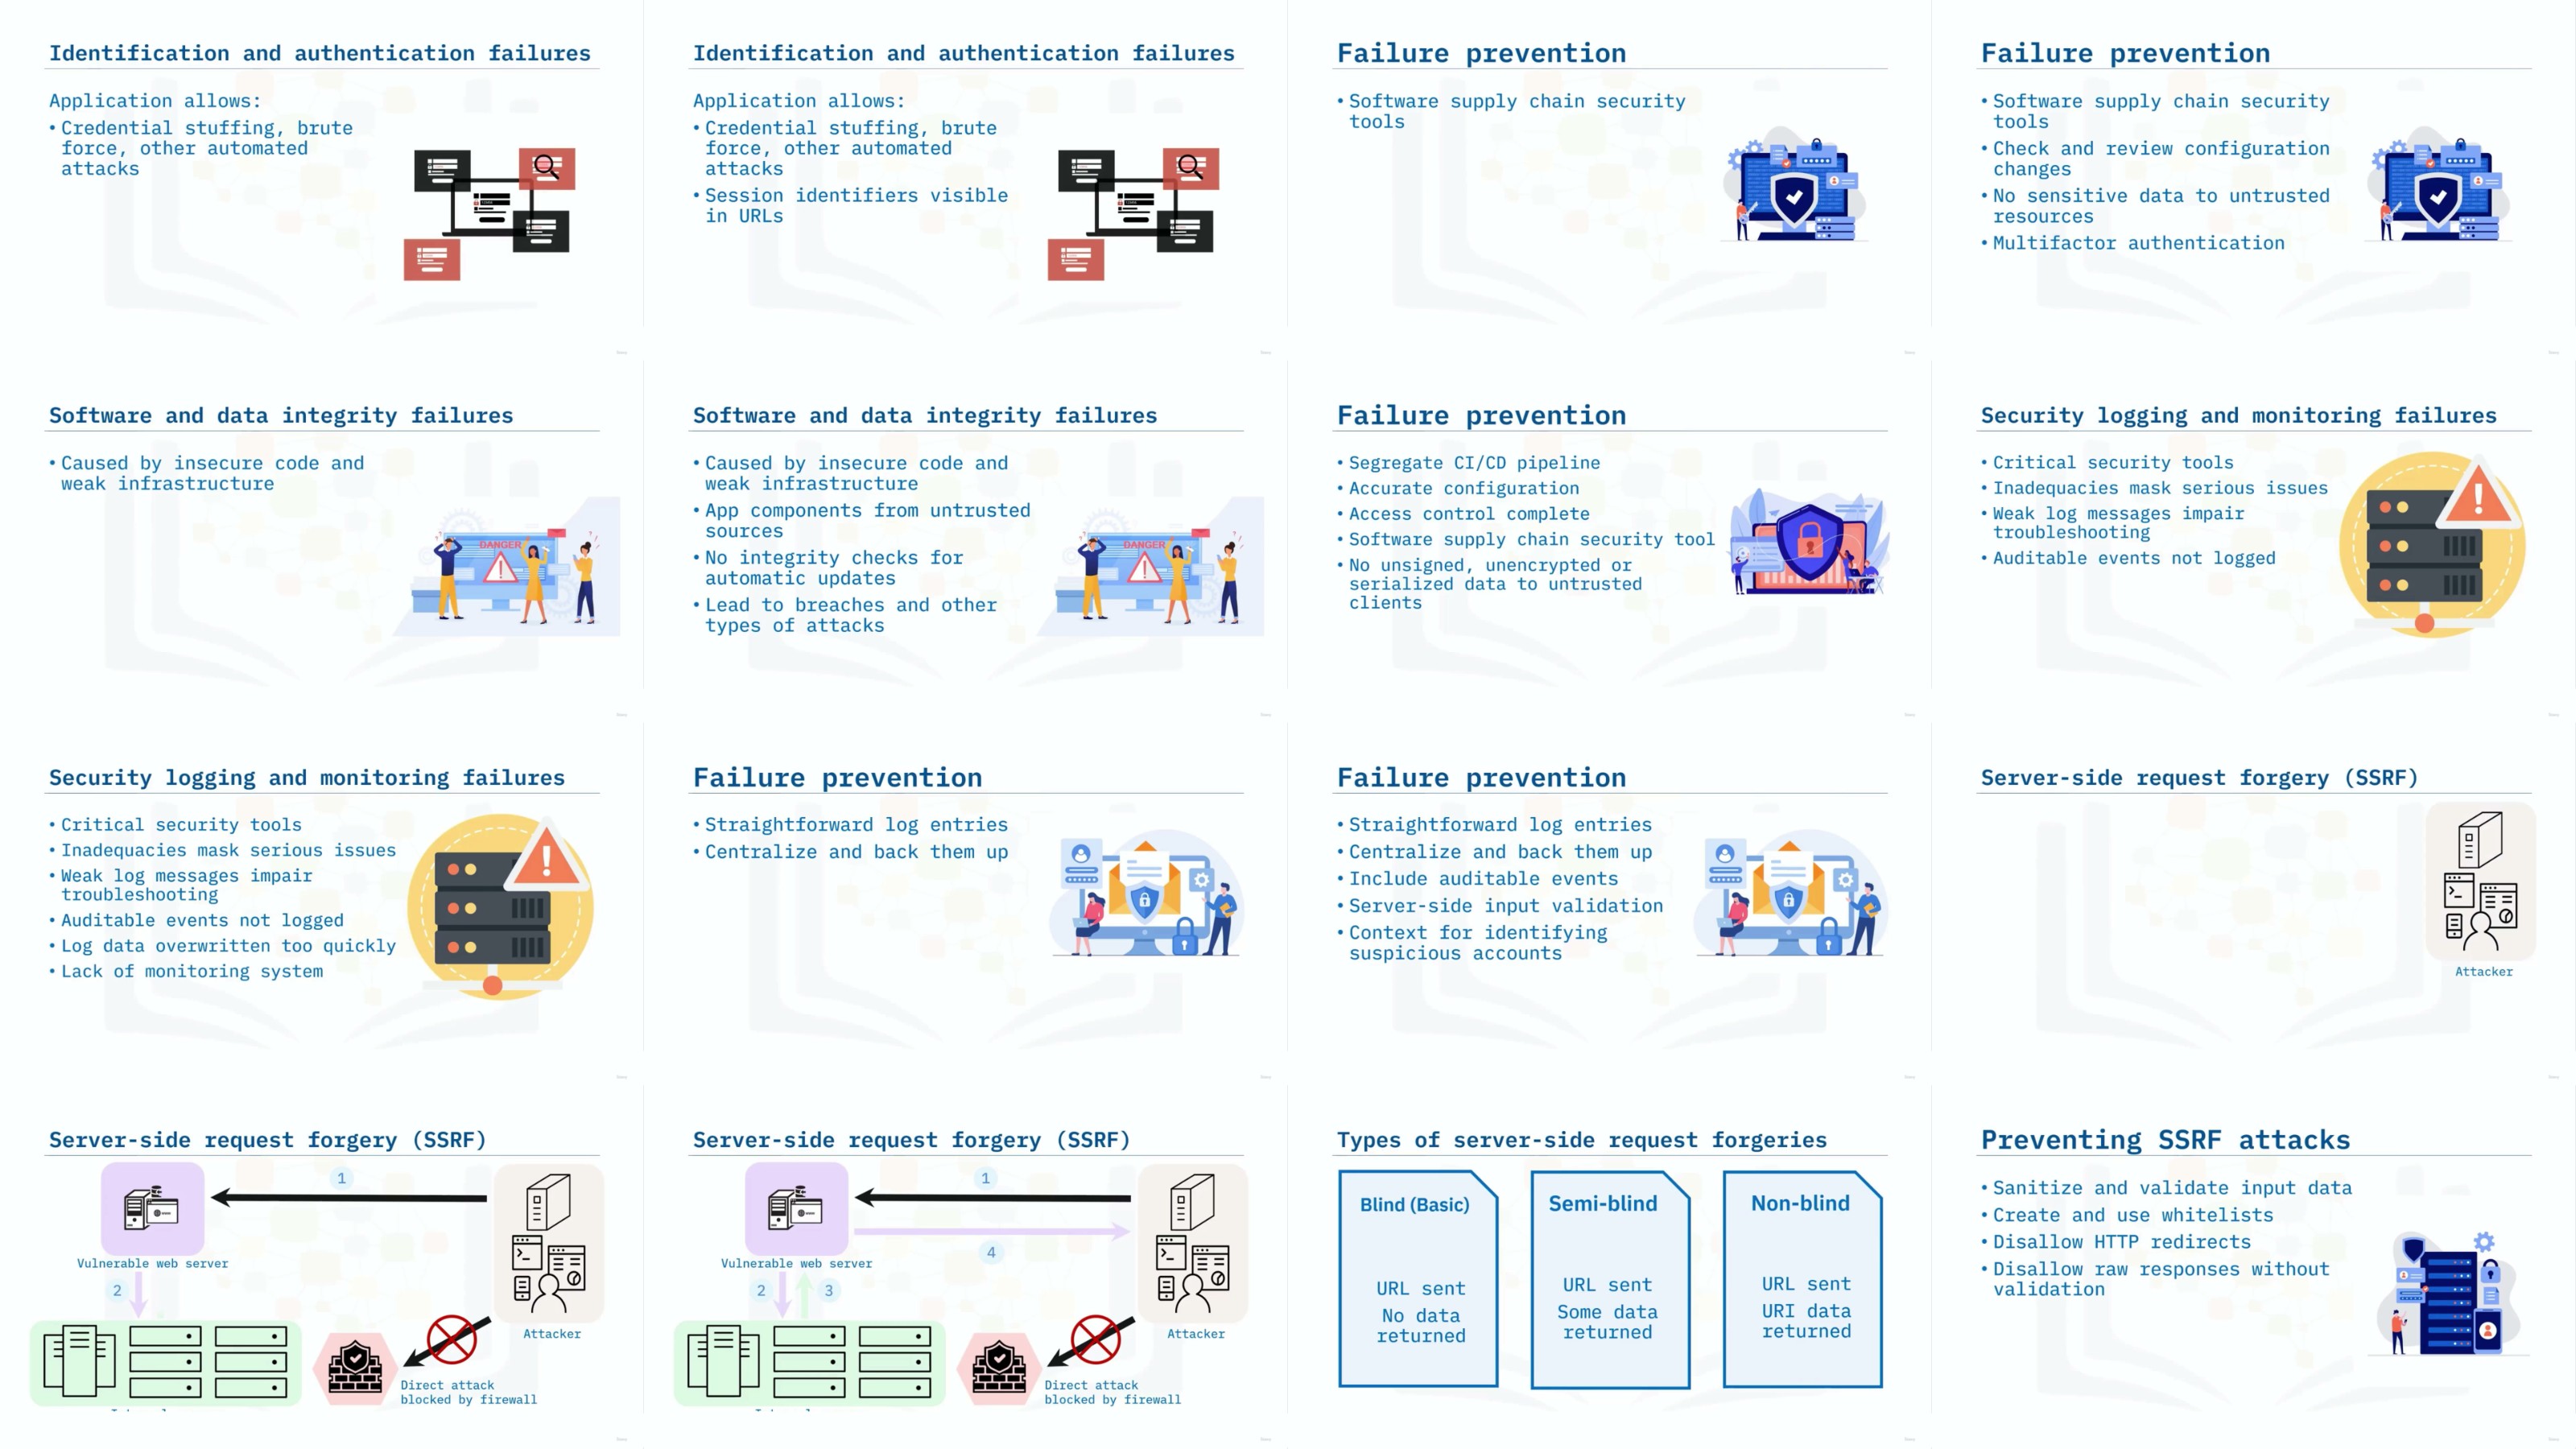
OWASP Top 10 Security Risks
The
OWASP Top 10
is one of the most important security references for web application developers and cybersecurity professionals.
You will explore the major OWASP risks along with practical concepts related to:
OWASP Top 10
SQL Injection Attacks
Advanced SQL Injection Techniques
Cross-Site Scripting (XSS)
Secure Secrets Management
Rather than simply memorizing vulnerability names, you will understand
why vulnerabilities occur, why they are dangerous, and how secure development practices can help prevent them
.
Secure Coding Best Practices
Secure applications start with secure code.
You will learn important principles for developing software with security in mind, including:
Secure Coding Practices
Secure Dependency Management
Building a Secure Development Environment
You will learn how to incorporate security into everyday development, reduce risks from third-party components, and create a more security-conscious development environment.
Application Monitoring Fundamentals
Security does not end when an application is deployed.
Modern applications must be
observed, monitored, measured, and continuously evaluated
.
You will learn about:
Application Monitoring
Types of Monitoring
Golden Signals of Monitoring
Monitoring vs. Evaluation
Monitoring System Components
Monitoring Metrics
Why Monitoring Matters
You will understand how monitoring can help identify performance problems, failures, unusual behavior, and potential security-related events.
Monitoring Systems & Techniques
You will explore modern application monitoring concepts and technologies, including:
Application Monitoring Tools
Software Metrics
Prometheus
Grafana
Monitoring Visualization
Alerting
Incident Response
You will learn how metrics can be collected, analyzed, visualized, and transformed into
clear and actionable insights
.
Logging & Course Completion
Logs provide valuable information about application behavior.
You will learn the fundamentals of application logging and important logging practices that can support:
Troubleshooting
Application Monitoring
Security Analysis
Incident Investigation
Operational Visibility
Detection of Unusual Activity
The course brings together
application security, secure development, monitoring, logging, alerting, and incident response
into one complete learning experience.
What You Will Learn
Throughout the course, you will develop knowledge of:
Application Security
Security by Design
DevSecOps
Threat Modeling
Vulnerability Scanning
SAST and DAST
Secure Code Review
Vulnerability Analysis
Runtime Protection
Software Composition Analysis
OWASP Top 10
SQL Injection
Cross-Site Scripting (XSS)
Secure Secrets Management
Secure Coding
Secure Dependency Management
Application Monitoring
Golden Signals
Monitoring Metrics
Prometheus
Grafana
Visualization
Alerting
Incident Response
Application Logging
Logging Best Practices
Continuous Security Analysis
Whether you are a developer who wants to write
more secure code
or a cybersecurity professional interested in
application security and monitoring
, this course provides a structured foundation for developing security-focused skills.
Why Application Security Matters
Modern applications depend on databases, APIs, cloud platforms, third-party libraries, authentication systems, and external services. Each component can introduce potential security risks.
Modern security therefore requires a
multi-layered approach
combining:
Secure Design + Secure Coding + Security Testing + Vulnerability Management + Monitoring + Logging + Alerting + Incident Response
This course helps you understand how these areas work together to create a stronger security strategy.
Build a Security-First Mindset
Instead of asking:
"Can we secure the application after development?"
A security-focused team asks:
"How can we build security into every stage of development?"
Throughout this course, you will explore how
DevSecOps, secure coding, security testing, vulnerability analysis, monitoring, logging, and incident response
work together throughout the application lifecycle.
Start Your Application Security Journey
If you want to understand
how secure software is designed, developed, tested, monitored, and maintained
, this course provides a comprehensive learning path.
Learn the principles of
Application Security, DevSecOps, OWASP Top 10, Secure Coding, SAST, DAST, SCA, Threat Modeling, SQL Injection, XSS, Secure Secrets Management, Prometheus, Grafana, Monitoring, Logging, Alerting, and Incident Response.
Take the next step toward becoming a
security-conscious software developer, DevSecOps professional, cybersecurity practitioner, or application security professional
.
Build better software. Build more secure software. Monitor it continuously. Make security an integral part of the software development lifecycle.

RapidGator
DDownload
NitroFlare

